How to Onboard an MSP Client Without Missing Critical Details
August 23, 2026 · 1590 words
Published by Steven Delaney
Client onboarding is where an MSP turns promises into operating responsibility. Sales conversations may establish scope, outcomes, and price, but onboarding must convert those agreements into working access, accurate records, monitored systems, support routes, and clear ownership.
Rushing that transition creates problems that can remain hidden for months. A backup may exist without a successful restore test. A critical application may depend on a former employee. An alert may still go to the previous provider. The MSP appears to own the environment while important responsibilities remain unassigned.
A strong onboarding plan does more than collect passwords and deploy agents. It reduces uncertainty in a controlled sequence, protects the client during the handover, and gives the service team enough context to support the business from the first day.
Define the finish line before discovery starts
Onboarding needs a clear definition of complete. Without one, the project becomes a list of setup tasks and ends when the calendar says it should, even if service gaps remain.
Define completion across several outcomes:
- Contracted systems and users are identified and matched to the agreed scope.
- Required administrative access is stored securely, tested, and assigned to accountable roles.
- Monitoring, backup, security, and service management controls are active and reporting correctly.
- Critical business services, dependencies, vendors, and recovery expectations are documented.
- Users and client leaders know how to request support and escalate urgent issues.
- Known risks, exclusions, and unresolved items have owners and target dates.
- The steady-state service team has accepted responsibility from the onboarding team.
Translate the sales agreement into this acceptance list before scheduling technical work. If a promised outcome cannot be tested, clarify what evidence will show it has been achieved.
Include the client in defining the finish line. Technical readiness matters, but so do user confidence, leadership visibility, and business continuity. This creates the foundation for the kind of client partnership built on shared responsibility rather than a one-sided technology handoff.
Establish one plan and one accountable owner
Appoint one onboarding owner within the MSP. That person does not perform every task, but they maintain the plan, resolve dependencies, track risk, and keep both sides informed. The client should also name one decision maker who can arrange access, coordinate employees, and confirm business priorities.
Build a single transition plan with phases, owners, dependencies, evidence, and due dates. Keep technical tasks, client tasks, and third-party tasks visible in the same plan so delays do not disappear between organizations.
At kickoff, confirm:
- Scope, exclusions, locations, users, and supported hours.
- Contract start date and the exact date operational responsibility transfers.
- Contacts for leadership, finance, security, operations, and urgent decisions.
- Incumbent provider responsibilities and knowledge-transfer arrangements.
- Planned changes that should pause during discovery.
- Communication frequency, meeting schedule, and escalation route.
- Conditions that could delay or stop the transition.
Avoid promising a seamless handover before discovery. The goal is controlled continuity, not the appearance that no uncertainty exists.
Discover the business before inventorying devices
Technical discovery is more useful when the MSP first understands what the client must keep operating. Ask leaders which services generate revenue, support customers, meet contractual obligations, protect sensitive information, or create major disruption when unavailable.
Map those business services to people, applications, identities, devices, networks, data, vendors, and facilities. This reveals dependencies that an automated scan cannot explain. A small desktop may run a label printer required for every shipment. A cloud application may rely on an integration managed by an outside consultant.
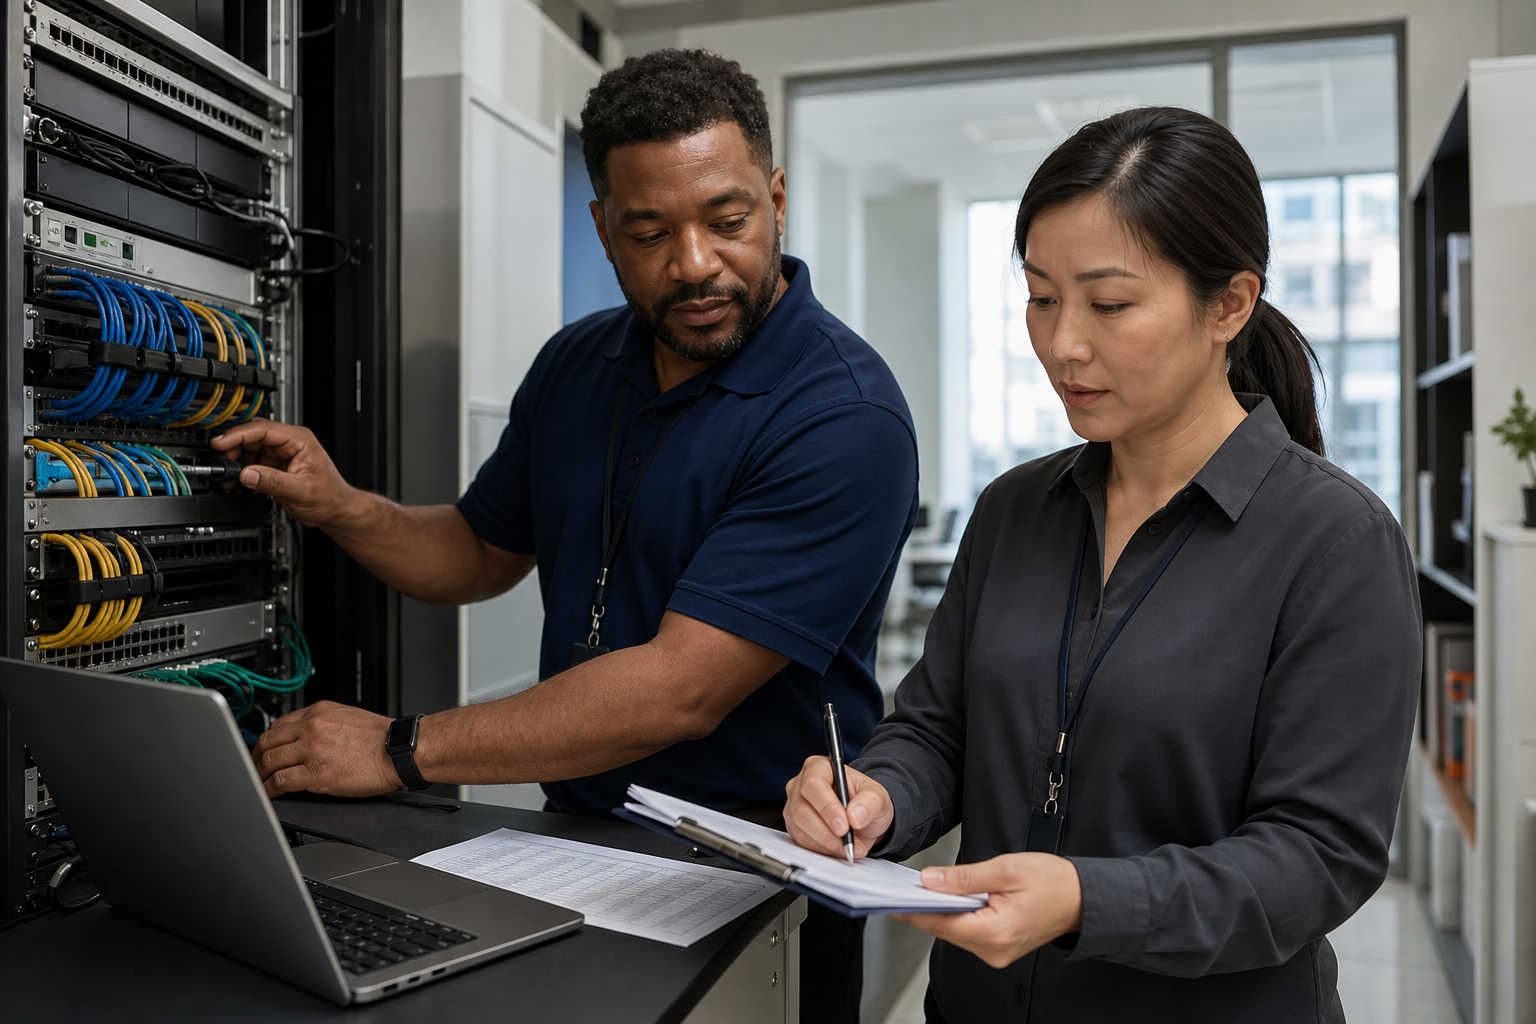
Then inventory the environment. Record assets, operating systems, warranties, network equipment, internet services, domains, cloud tenants, business applications, backup targets, security tools, certificates, licenses, and vendor contracts. Compare automated findings with invoices, interviews, and physical inspection.
Treat missing information as a risk, not an empty field to complete later. Good onboarding depends on the same documentation discipline that protects service continuity. Record the source and verification date for important facts so the service desk can judge whether they remain reliable.
Transfer access without creating shared uncertainty
Access transfer is one of the highest-risk parts of onboarding. Do not accept a spreadsheet of passwords as proof that control has moved safely.
Create an access register covering domains, identity platforms, cloud services, network equipment, security tools, backup systems, vendor portals, applications, and emergency accounts. For each path, identify the owner, purpose, privilege level, authentication method, recovery route, and test status.
Use named accounts where platforms support them. Apply least privilege, require multifactor authentication, protect emergency credentials, and record approval for elevated access. Test access before the outgoing provider or internal administrator loses it. A credential that has been received but never used is still an unknown.
Plan the removal of obsolete access as carefully as new access. Confirm when former provider accounts, shared credentials, API tokens, remote tools, and vendor contacts can change without interrupting the transition. The principles in a secure MSP client offboarding process apply because the same handover has two sides: one provider gains responsibility while another gives it up.
Keep an audit trail of each transfer. If access cannot be verified, assign a named owner, deadline, business impact, and fallback route rather than quietly marking the task complete.
Stabilize first, improve second
Onboarding often reveals aging systems, weak controls, and unsupported software. Fixing every issue during the transition creates too much change when the MSP understands the environment least.
Separate work into three groups:
- Immediate protection: actions required to prevent likely harm or maintain service during transfer.
- Onboarding baseline: controls needed to deliver the contracted service, such as monitoring, backups, endpoint management, alert routing, and support integration.
- Future improvement: projects that need design, budget, testing, or broader client decisions.
Prioritize by business impact, urgency, dependency, and reversibility. Avoid large infrastructure changes unless delay creates a greater risk than change. Use a controlled change window, a rollback plan, and confirmed client approval for anything that could interrupt operations.
Create a risk register for gaps that will remain after service begins. State the current condition, possible impact, temporary control, recommended action, owner, and review date. This prevents onboarding from becoming an unrecorded promise to resolve everything later.
Prepare the service desk for day one
Deploying tools does not make the steady-state team ready. The people who will answer tickets need concise, verified operating context.
Before service activation, brief the team on:
- Client business, locations, working hours, and critical services.
- Supported users, systems, and explicit exclusions.
- Common requests, known problems, and approved workarounds.
- Important contacts, communication preferences, and authorization rules.
- Priority definitions, escalation paths, and update expectations.
- Vendor dependencies and how to engage them.
- Security, privacy, compliance, and change-control requirements.
- Remaining onboarding risks and temporary procedures.
Run a scenario review using likely incidents: a locked-out executive, failed internet circuit, unavailable business application, suspicious login, or backup alert. This exposes missing permissions and unclear ownership before a user is waiting.
Test the support experience from the client's side: portal or email route, phone handling, ticket acknowledgment, urgent escalation, and notifications. Tell employees what is changing, when support begins, and how to get help.
Use a controlled service activation
Choose a clear activation point rather than letting responsibility drift across several days. Confirm that the MSP, client, and outgoing provider understand who owns monitoring, incidents, backups, changes, and vendor communication at that time.
Use an activation checklist and obtain explicit acceptance from the onboarding owner and service owner. Critical alerts should reach the correct queue. Backup jobs should report their real status. Remote access should work. Client contacts should be reachable. Open risks should be visible. Support staff should know the environment is live.
Maintain increased review during the first few weeks. Watch recurring requests, failed automation, missed alerts, user confusion, and documentation gaps. Early patterns may show that training, configuration, capacity, or scope needs attention.
Do not measure stabilization only by a decline in tickets. A quiet queue can mean users do not know how to reach the MSP. Look at acknowledgment times, reopened issues, monitoring coverage, backup results, unresolved onboarding tasks, user feedback, and progress against known risks.
Close onboarding with evidence and a roadmap
Onboarding should end with a formal transition to normal service. Review the original acceptance criteria and show evidence for each outcome. List incomplete items, accepted risks, future projects, owners, and dates. Confirm that temporary accounts, files, communication channels, and elevated permissions created for onboarding have been removed or assigned a continuing purpose.
Provide the client with a concise summary of the environment, support routes, major risks, completed controls, and next priorities. Feed improvement work into the regular roadmap rather than leaving it in the onboarding project. The first technology business review can then evaluate progress against a known baseline instead of recreating discovery.
Finally, hold a short retrospective. Identify what caused delays, which information arrived late, where responsibility was unclear, and what should change in the onboarding template.
A successful onboarding does not mean the environment is perfect. It means responsibility is explicit, critical services are understood, access and controls are verified, risks are visible, users can obtain help, and the service team is ready to operate. That is the point where a new contract becomes a dependable managed service.
Steven Delaney
MSP Industry Expert • Houston, TX
Strategic insights and practical guidance for the modern Managed Service Provider. Based in Houston, TX.